
More Than 300 Tor Exit Relays Were Hijacked to Steal SSH Passwords, and Nobody Knows Who Did It
An unknown attacker took over more than 300 Tor exit relays in early October, many on servers backdoored with the Ebury OpenSSH malware, and redirected SSH logins to a dozen servers that harvested passwords.

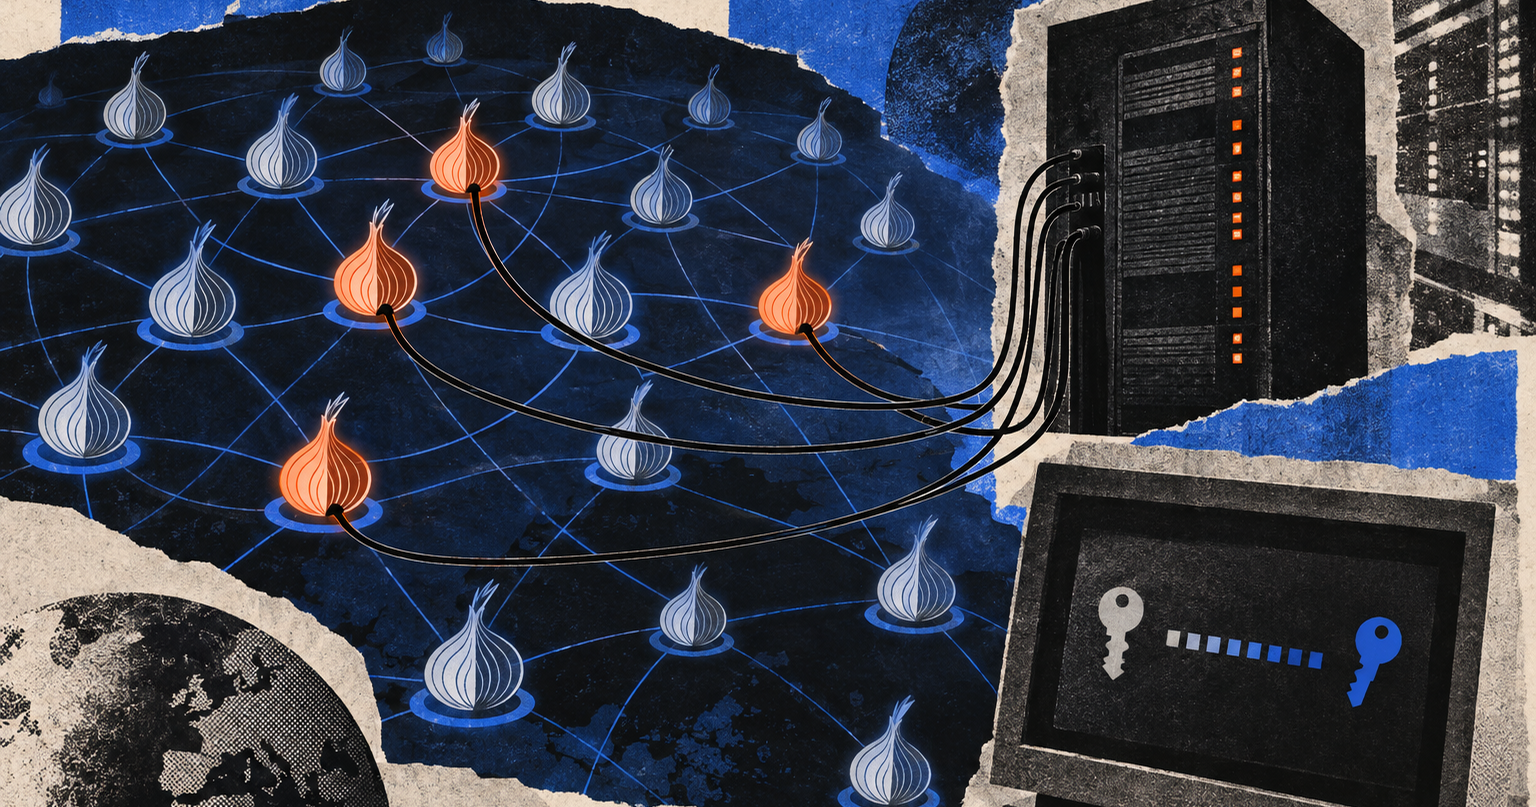
For about three days in early October, someone quietly controlled a large slice of the Tor network's exit relays, the last hop where anonymized traffic leaves Tor and reaches the open internet. They used them to reroute SSH logins to a dozen interception servers that collected passwords and watched sessions in real time.
The attacker did not need to run a single relay of their own. They broke into the volunteers' servers instead, many of them backdoored with Ebury, an OpenSSH backdoor that has been around since 2009. Tor's whole model rests on volunteers running honest relays. Here, honest relays were simply taken over.
Risky Bulletin called it one of the largest security incidents in Tor's history. Who did it, how most of the servers were entered, and how many people lost passwords are all still unknown.
One changed key warning
The researcher known as kaba noticed on the morning of October 2, when an SSH connection over Tor came back with a changed host key warning. He scanned all of Tor's roughly 3,000 exits with exitmap and found 333 of them redirecting SSH to the same 12 servers. He reported it to Tor's network health team that evening.
The attackers had rewritten the relays' torrc configuration to allow port 22, switching on SSH exit traffic on 342 relays that had blocked it. Another 24 relays that had never been exits were turned into exits. The same edit closed the encrypted mail ports for IMAPS and POP3S, and on most relays opened plaintext POP3 and IMAP. "It seems the attacker is gaining access to Linux based hosts," the Tor Project wrote in an October 5 notice, adding that non-exits were being converted "to be able to carry out the SSH attack."
The theft only worked on some logins. About a dozen exits served a fake host key in kaba's scan, and a user who accepted it and typed a password handed that password over. The interceptor then connected to the real server, so the session worked normally while every command could be watched. Separately, the attacker logged in with the stolen password, checked for sudo and ran a base64 encoded Perl installer. Key-based logins could not be relayed to the real server this way. Anyone who accepted a changed host key over Tor in that window should consider the password they typed stolen.
How big, and how it ended
The figures depend on how you count. At its peak the attacker's policy held 7.46% of Tor's exit capacity by consensus weight, while Risky Bulletin counts more than 10% of exit relays by number. A directory analysis reported by The Hacker News found 377 relays from 59 operators that switched to the attacker's exit policy, which it calls "a policy match, not proof of compromise."
Tor's health team had spotted the policy change too. On October 4 it contacted Zimmer, who ran the Quetzalcoatl relay family, the largest affected group, and he confirmed the change was not his. Directory authorities began voting BadExit flags at 18:00 UTC that day. On the morning of October 5, a scripted restart nobody can explain swept 55 Quetzalcoatl hosts with the policy still in place. By 17:00 UTC no relay with the attacker's policy remained in the consensus, and none had returned by October 9. Tor Metrics' count of exits fell by about 370 between October 3 and 5 and had not recovered by October 18.
For comparison, in November 2023 Tor removed more than 1,000 relays tied to a for-profit crypto scheme.
One reused password
Zimmer's October 7 post-mortem is unusually blunt. Two of his servers ran Ebury 1.8.3. On August 28 the attacker logged in to his management server with the operator password on the first try, had root within five minutes and installed Ebury. "The root cause was ours: one password reused for SSH login, sudo and the backup passphrase, stored in plaintext on both servers, plus SSH password authentication left enabled on the internet-facing management server," he wrote. The family's "offline" master keys "were not offline."
ESET estimated in 2024 that Ebury had infected 400,000 servers. Version 1.8.3 is newer than ESET's public indicators, so Marc-Etienne Léveillé, who wrote ESET's Ebury research and has since left the company, posted an updated detection script. "Given how many servers had Ebury between 2009 and 2023 (400 000!), there are most likely other compromised Tor relays out there," he wrote.
Hijacking someone else's machine to profit from its network position is a familiar trick; attackers have been taking over NAS boxes and camera recorders to resell their internet connections. What remains unexplained here is how the other 58 operators were entered. One clue stands out: 71 of 101 relays hosted at FranTech Solutions (BuyVM) switched policy, against 13 of 9,054 elsewhere. "Could they have compromised those servers at the hoster level?" kaba asked on the Tor mailing list.
Nobody has answered that yet. Nobody has attributed the campaign either, and no one knows how many passwords walked out the door.
Some offers on this page may be paid placements or contain affiliate links.
Cyberpresso: daily cyber & AI brief
Free daily newsletter, read in 5 minutes.
Subscribe free