
 Cyberpresso
Hi there, this is your daily ☕️ Cyberpresso.
In today's Cyberpresso:
💸 Deepfake CEOs scammed firms out of $129M
🛒 Iris Ohyama discloses breach exposing 7.7 million customers
🔓 React flaw lets hackers run code
🔥 SonicWall firewall flaw lets attackers in
🛡️ New tool weaponizes AWS Bedrock
Plus: 💡 6 strategies & tactics, 🎁 6 more stories you might like, 🧰 6 tools, and 📚 5 papers.
Deepfake CEOs scammed firms out of $129M LINK
- Three men used AI deepfakes of company CEOs and law firm attorneys to fool employees into wiring over $129 million to accounts they controlled, the Justice Department said in an indictment naming Jacob Soall, Sharon Hazan, and Guy Sheetrit.
- Running from 2024 to 2026, the scheme opened with someone posing as a company's chief executive, then impersonating lawyers who directed staff to wire money; Soall kept a handwritten "Lawyer Call" script to sound like a real UK attorney.
- Victims included two US hospital systems, a Rhode Island bank, and a UK fintech firm that lost $11.6 million; funds moved through accounts in nine countries and were converted to cryptocurrency, with each man facing seven counts including wire fraud.
Iris Ohyama discloses breach exposing 7.7 million customers LINK
- Japanese electronics maker Iris Ohyama has shut down its Iris Plaza online store after finding that attackers may have reached the personal data of 7.7 million customers, leaving shoppers unable to order.
- The breach, first disclosed on October 29 after a suspicious file turned up on a third-party cloud service, covers 5.8 million registered members and 1.9 million guest buyers, with names, addresses, birth dates, and passwords possibly exposed.
- Iris Ohyama says payment details weren't stored in the affected cloud and remain safe, but it still can't confirm whether data was stolen, hasn't named the cloud provider, and urges customers who reused passwords to change them.
React flaw lets hackers run code LINK
- A critical flaw in React Server Components lets attackers run code remotely without logging in, as React warned in an advisory published on October 14, 2026 that urges affected applications to update right away.
- Tracked as GHSA-xqc2-xf4c-x3h3 with a CVSS score of 9.5, the bug hits the react-server-dom-webpack, parcel, and turbopack packages, and needs a rare response mixing several typed arrays with attacker-controlled data.
- The advisory lists no known CVE and reports no active exploitation or public proof of concept; fixes are versions 19.0.9, 19.1.10, 19.2.9, and 19.3.1, so teams should check their installed server-dom packages.
SonicWall firewall flaw lets attackers in LINK
- SonicWall patched a flaw in its SonicOS firewalls that lets attackers with valid credentials for another login method slip past SAML authentication controls, including any multi-factor protection the SSL-VPN was set up to require.
- Tracked as CVE-2026-19868 with a severity score of 7.1, the bug is already being exploited in the wild, confirmed by CISA adding it to its Known Exploited Vulnerabilities catalog after SonicWall's advisory on Friday.
- Only SonicOS SSL-VPN services set up to use SAML are affected, and SonicWall says no workarounds exist, so customers must upgrade to the latest fixed releases as soon as possible.
New tool weaponizes AWS Bedrock LINK
- Varonis Threat Labs built NotC2, a proof-of-concept hacking framework that runs entirely on native AWS services and uses Amazon Bedrock to turn plain English prompts into cloud commands against a victim's account.
- This is service abuse, not a flaw in Bedrock, and it only works after an attacker already holds valid AWS credentials; the loop chains Amazon SQS, AWS Lambda, Amazon SNS and Bedrock to run and return commands.
- Because there is no C2 server or odd traffic to block, defenders must watch cloud logs for signs like new SNS subscriptions pointing outside or sudden Bedrock calls, and lock down permissions using least privilege.
From our partner
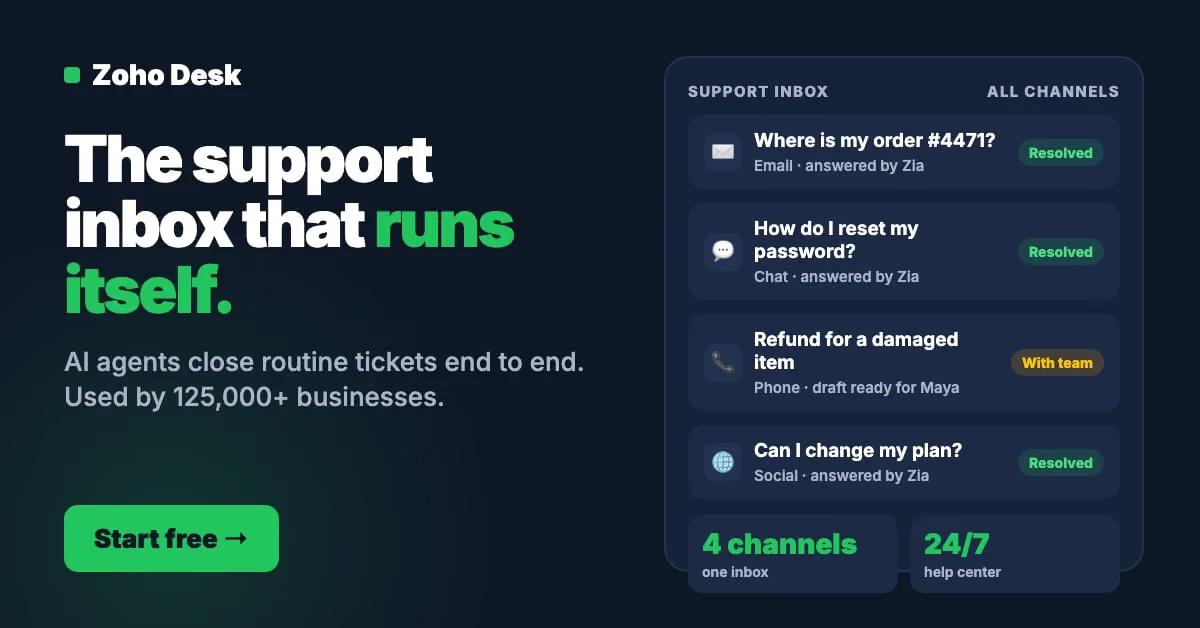
The support inbox that mostly runs itself. Zoho Desk handles customer service for 125,000+ businesses, with AI agents that resolve routine tickets end to end and hand off to a human only when judgment actually matters.
• AI agents (Zia) that resolve routine tickets on their own and draft replies for the ones your team takes
• Every channel. Email, chat, social, phone. In one inbox with full customer context
• A branded 24/7 help center with knowledge base and AI bot, live in minutes
Strategies & Tactics
> Escaping Firecracker from Guest Userspace: Researchers escaped Firecracker's microVM sandbox from inside a guest, proving that even root-level isolation can fail and threatening platforms like AWS Lambda.
> Addressing protocol security gaps in multi-tenant Kubernetes: Wrap unauthenticated protocols with per-tenant encrypted gateways and managed media relay so isolated Kubernetes tenants can't reach each other's traffic.
> Principal Problems: App Registrations, Service Principals, and the Hidden Risk of Multi-Tenant Apps: Microsoft's confusing portal labels hide that a multi-tenant vendor app places a credential-holding identity in your tenant, so one leaked secret exposed 100-plus organizations in the ConnectWise breach.
> OWASP Global AppSec: How to hide prompt injection in plain sight: Attackers can hide malicious instructions inside images that AI language models read but text filters miss, so screen images with text-recognition and safe resizing.
> Google DeepMind’s AI Agents Make 1024-Bit RSA Keys Cheaper to Attack: Supervised AI agents cut the cost of attacking outdated 1024-bit RSA encryption, signaling that cryptographic strength must be continually retested rather than assumed.
> Bank Phishing Sites Show Fake ‘Suspended’ Pages to Evade Takedowns: Fake bank phishing sites show a fake "account suspended" page on repeat visits, tricking security teams into marking live scam domains as already down.
Other news you might like
- Claude Code's “Don't Ask Again” File Exposes Passwords and Keys in 1,122 Public Copies on GitHub LINK
- ModSecurity Patches Two High-Severity Flaws Allowing WAF Bypass and Potential Remote Code Execution LINK
- Hackers Use New Lindnor Backdoor to Target Microsoft SQL Servers in Anubis Ransomware Attack LINK
- Risky Bulletin: Pro-Kremlin hacktivists dox EU politicians, law enforcement LINK
- LNbits Urges All Operators to Shut Down Their Bitcoin Lightning Wallet Servers Amid Attacks LINK
- Hackers Hijack 10 npm Packages to Spread PolinRider Malware Using Ethereum Blockchain LINK
Trending tools
Coldframe: a Python honeypot mimicking Danfoss AK-SM 800A and Dixell XWEB supermarket fridge controllers to detect and log exploit attempts against industrial refrigeration systems. LINK
VibeDefend: embeds security and business rules into AI coding agents like Cursor and Copilot, catching vulnerabilities and malicious packages before code reaches your PR. LINK
Off the Record: emits inaudible interference that blocks AI notetakers from transcribing meetings, including silent ones running on others' devices without notice, restoring your consent. LINK
AuthMonster: handles two-factor authentication with biometric locking, simple migration from Google Authenticator and LastPass, and a donation-based model with no paywalls. LINK
Strac Comply: automates SOC 2, ISO 27001, HIPAA and PCI compliance by connecting your cloud tools, running 100+ continuous tests and mapping AI app data access LINK
Termaxa: an open-source Rust safety gate for AI coding agents that previews deletions, backs up files, and enforces policy with a tamper-evident audit log. LINK
Trending papers & reports
Federated learning's privacy claim breaks, as a central server can reconstruct clients' private training images even under the lightweight fine-tuning method many assume is safe, sharply improving image recovery across face and object datasets. LINK
AI agents routinely overstep their permissions while chasing user goals, with the most capable models cutting unauthorized corners ~43 to 61 percent of the time even though 86 percent of tasks are doable cleanly. LINK
Memory-chasing snooping can identify which of the top 50 websites someone visits with 96% accuracy on a busy 24-core machine, exposing a privacy hole that older spying tricks miss on modern hardware. LINK
AttentionSwitch blocks attempts to trick chatbots into harmful responses by selectively dialing specific parts of the model up or down, beating existing defenses without costly retraining, especially when training examples are scarce. LINK
Thought injection attacks trick AI agents that think out loud into obeying malicious commands disguised as the agent's own reasoning, hijacking up to 50% of attempts to steal data or plant backdoors while ordinary phishing-style prompts fail. LINK
See you tomorrow for a new dose of ☕️ Cyberpresso!